This guide explains BIP 70 Payment Protocol in plain English. It covers the problem behind the BIP, why it matters and whether the proposal is part of Bitcoin today.
TL;DR
What it is: BIP 70 defined a merchant-to-wallet payment protocol using Protocol Buffers, HTTP or HTTPS and optional X.509 identity. PaymentRequest described outputs and expiry, Payment carried signed transactions and refund outputs, and PaymentACK confirmed receipt.
Why it matters: BIP 70 offered authenticated requests and immediate acknowledgements, but its PKI, parser and refund model brought lasting operational risk. Existing records may require careful legacy interpretation; new payment systems should use maintained protocols with narrower trust boundaries.
Current position: Where the feature is closed or legacy, isolate the parser and record that limitation before testing.
BIP 70 Payment Protocol in simple English
BIP 70 Payment Protocol: The BIP set size recommendations for request, payment and acknowledgement messages. Protocol Buffer parsers, certificate libraries and HTTP clients expanded the wallet attack surface.
Simple example
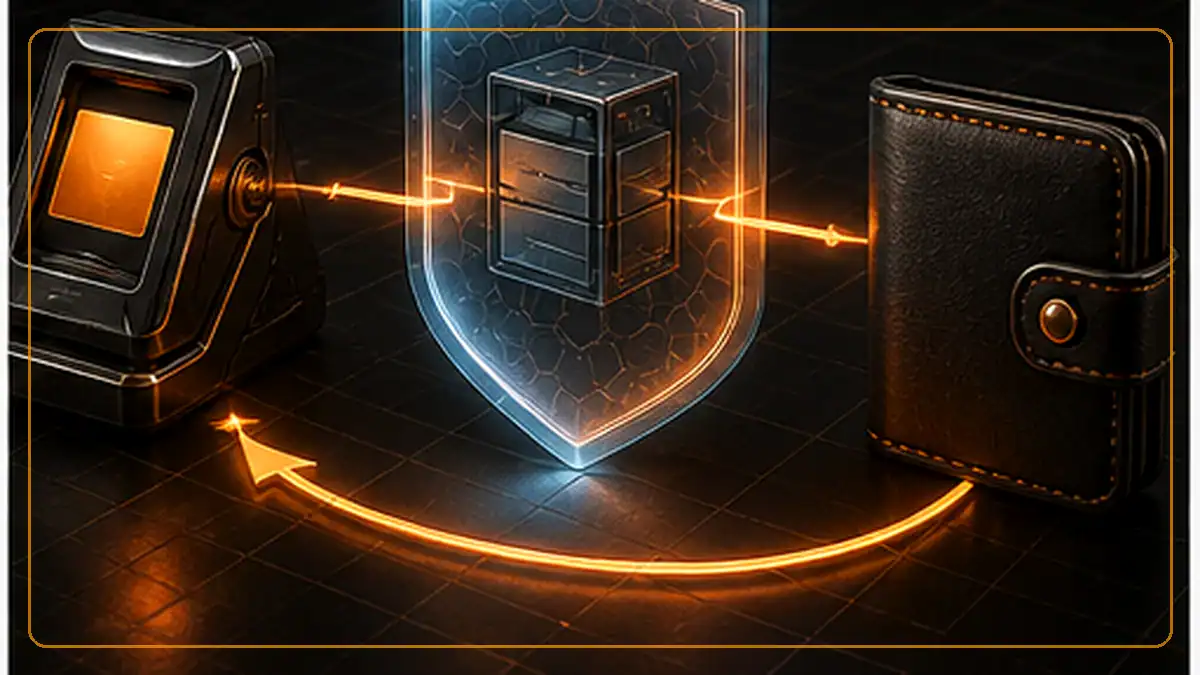
A node operator is checking BIP 70 Payment Protocol. Wallets had to reject unsupported networks, expired requests and oversized messages before asking for authorisation. A merchant returned a PaymentRequest, the wallet validated and displayed it, the customer authorised payment, and the wallet optionally posted a Payment to the payment URL.
Key terms in plain English
BIP:
Bitcoin Improvement Proposal: a document describing a proposed rule, standard or process. Its status must be checked separately.
Bitcoin Core:
Widely used software that validates Bitcoin and can provide wallet, network and operator tools.
Node:
A computer running Bitcoin software that checks data and communicates with other peers.
Three-message sequence
A merchant returned a PaymentRequest, the wallet validated and displayed it, the customer authorised payment, and the wallet optionally posted a Payment to the payment URL. The merchant answered with PaymentACK. Broadcast and merchant acknowledgement were related but separate; a failed HTTP response did not necessarily mean the Bitcoin transaction was absent.
PaymentRequest contents
PaymentDetails named the network, one or more amount-and-script outputs, creation time, optional expiry, memo, payment URL and opaque merchant data. A wrapper added version, PKI type, certificate data and signature. Wallets had to reject unsupported networks, expired requests and oversized messages before asking for authorisation.
Merchant identity and X.509
The optional PKI mode signed the serialised request with a key certified through the web public-key infrastructure. Successful validation associated the request with a certificate identity, not with the truth of every commercial claim. Certificate expiry, revocation, compromised authorities, hostname interpretation and legacy SHA-1 support all affected assurance.
Merchant identity and X.509: the fields, validation boundary and operational evidence that implementations need to agree.
Payment and refund outputs
Payment carried the satisfying transaction or transactions, merchant data, a memo and refund_to outputs. Refund destinations supplied by a compromised client or altered connection could divert later refunds. A merchant needed to authenticate order state and use a current, independently confirmed refund process rather than treating old refund outputs as timeless authority.
Acknowledgement and retry
PaymentACK echoed the Payment and could include a status memo. Servers were expected to acknowledge repeated identical Payment messages so a transport failure could be retried. Idempotency is essential: a retry must not create a second order, refund or accounting event merely because the client did not receive the first acknowledgement.
Resource and dependency risks
The BIP set size recommendations for request, payment and acknowledgement messages. Protocol Buffer parsers, certificate libraries and HTTP clients expanded the wallet attack surface. Redirects, MIME handling and payment URLs required strict controls. A checkout should not revive unmaintained parsing code simply to support a historical merchant flow.
How specialists test it
Developers test the proposal with made-up data on an isolated test network. They check normal cases and deliberately invalid cases. Different implementations should reach the same result before anyone relies on the proposal.
Frequently asked questions
What is the main point of BIP 70 Payment Protocol?
BIP 70 Payment Protocol: The BIP set size recommendations for request, payment and acknowledgement messages.
For BIP 70 Payment Protocol, what should a beginner know about three-message sequence?
A merchant returned a PaymentRequest, the wallet validated and displayed it, the customer authorised payment, and the wallet optionally posted a Payment to the payment URL.
For BIP 70 Payment Protocol, what should a beginner know about paymentrequest contents?
PaymentDetails named the network, one or more amount-and-script outputs, creation time, optional expiry, memo, payment URL and opaque merchant data.
For BIP 70 Payment Protocol, what should a beginner know about merchant identity and X.509?
The optional PKI mode signed the serialised request with a key certified through the web public-key infrastructure.
Conclusion
BIP 70 offered authenticated requests and immediate acknowledgements, but its PKI, parser and refund model brought lasting operational risk. Existing records may require careful legacy interpretation; new payment systems should use maintained protocols with narrower trust boundaries.
Check the current specification status and the documentation for the exact implementation you operate before moving production funds or changing a mining node.
About the Author:
Darren Waggott is the visionary Founder and CEO of The Mining Shop UK, with over a decade of leadership in the cryptocurrency mining sector. Renowned for driving innovation, Darren has built a company dedicated to providing high-quality ASIC miners and comprehensive hosting services. His forward-thinking approach places The Mining Shop UK at the forefront of the industry.
Membership helps us protect the discussion from spam and keep answers useful.
ASIC MINING SUPPORT
Need Help Choosing an ASIC Miner?
Tell us what you want to mine, your electricity cost and where the machine will run. We can help you compare hardware, power requirements, hosting and repairs.
We use necessary cookies to run the shop and optional analytics cookies to understand how visitors use the site and improve shopping and checkout. You can accept analytics, use only necessary cookies, or choose settings. You can change your choice at any time.
Functional
Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes.The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.


Join the ASIC Mining Discussion
Members can read and join the discussion
Log in to read comments from other miners. Create a free account if you would like to ask a question or share your experience.
Membership helps us protect the discussion from spam and keep answers useful.