Build secure remote ASIC monitoring with a VPN, network segmentation, strong authentication, least privilege, logging, patching and a tested recovery route.
Remote ASIC monitoring with a VPN can keep miner administration off the public internet. But a VPN is only the access path. A secure design also separates miners from business and payment systems, authenticates the user and device, limits which management services are reachable, records changes and retains a local recovery route.
Publishing a miner web interface or forwarding its management port is not an acceptable substitute.
remote ASIC monitoring with a VPN in simple English
Remote ASIC monitoring with a VPN: List the actual tasks: view hashrate and temperatures, receive alerts, change pools, restart a miner, update firmware or control power.
Simple example
A mining technician is checking remote ASIC monitoring with a VPN. Read-only monitoring and administrative control should not automatically use the same account or network permission.
Key terms in plain English
ASIC:
A computer built to do one specialised job. A mining ASIC is designed for a particular proof-of-work algorithm.
Hashrate:
The amount of mining work a machine attempts each second. More hashrate does not guarantee more profit.
Mining pool:
A service that combines work from many miners and shares rewards using stated rules.
Share:
Proof sent by a miner to show completed work. A pool uses accepted shares when calculating rewards.
Firmware:
Software stored on the miner that controls its hardware. Use a trusted source and check model compatibility.
Map what remote monitoring must do
List the actual tasks: view hashrate and temperatures, receive alerts, change pools, restart a miner, update firmware or control power. Read-only monitoring and administrative control should not automatically use the same account or network permission.
Identify every component between the operator and the ASIC: laptop or phone, identity provider, VPN gateway, firewall, management server, switch, miner interface and pool. Record who owns and updates each one.
Keep payout-wallet private keys outside this path. A miner needs pool credentials and a payout destination in some configurations. But remote monitoring should not require custody of the keys that spend Bitcoin.
Quick reference for remote ASIC monitoring with a VPN.
Segment the mining network
Put ASICs and mining controllers on an operational segment separate from office laptops, customer records, finance, WooCommerce, Wi-Fi guests and other internet-connected devices. Enforce the boundary with firewall rules, not just different address ranges.
The NCSC describes network segmentation as fundamental to limiting the impact of compromise and lateral movement. Remote access should be mediated through a VPN appliance, proxy, connector or firewall under explicit policy rather than opening a route to a flat network.
Permit the miner segment to reach only the required pool, time, name-resolution, update and monitoring services. Review the exact endpoints because some firmware or management platforms use cloud services. Do not block required traffic blindly. But do not allow unrestricted outbound access by default.
Example remote-access permissions
Role
Allowed action
Denied by default
Viewer
Read dashboard and alerts
Pool, firmware and power changes
Operator
Restart and approved pool failover
Network and identity administration
Engineer
Time-limited diagnostic access
Payout wallet and office systems
Administrator
Gateway and policy maintenance
Routine daily use from unmanaged device
Vendor support
Approved session to named device
Permanent shared account
Choose the VPN or access architecture
A site-to-user VPN can work for a small on-premises mine when the gateway is maintained and correctly exposed. A site-to-site tunnel can connect a central operations network to a facility. A zero-trust access service can broker access to a particular monitoring application without placing the remote device broadly inside the site.
NCSC guidance notes that traditional VPN and zero-trust approaches are not mutually exclusive. It recommends authenticating remote devices and users and applying rules that prevent remote clients communicating with one another unless required.
Prefer a well-supported protocol and product with prompt security updates, secure key storage and an auditable configuration. Avoid installing an unknown convenience VPN directly on each miner or relying on an abandoned router image.
Use strong identity and least privilege
Give every person an individual account. Do not share an administrator password across staff, contractors and hosts. Use phishing-resistant or app-based multifactor authentication where the gateway supports it and protect recovery codes offline.
Bind access to managed devices where practical. Apply short session lifetimes for privileged work and time-limit third-party access. Remove leavers and expired contractors immediately rather than waiting for an annual review.
Routing should give a viewer access only to the monitoring service and an engineer only to the approved miner or subnet. A successful VPN connection should not mean unrestricted access to every device at the site.
Harden miner and management interfaces
Change default credentials, apply verified firmware through a controlled process and disable unused services. Inventory the firmware version and model because supported controls differ. Do not assume an internal HTTP interface encrypts credentials merely because the VPN tunnel is encrypted.
Use a management proxy or platform when it meaningfully reduces direct administration and provides roles, history and alerts. Secure that platform as a critical service. Centralisation can reduce exposure but increases the impact of one compromised account.
Never forward ports 80, 443, 22 or vendor management ports from the internet directly to an ASIC. Search-engine invisibility is not access control, and changing the port number does not remove the vulnerability.
Log changes and detect abnormal behaviour
Record VPN login, source device, authentication result, configuration change, pool destination, firmware update, power action and failed access. Synchronise clocks so the gateway, controller, pool and miner events can be correlated.
Alert on a new administrator, disabled multifactor authentication, unexpected country, repeated failure, new pool endpoint, payout change, firmware change or a miner communicating with an unapproved destination. Do not collect logs without deciding who reviews them and how long they are retained.
Protect logs from ordinary miner administrators so an intruder cannot erase the evidence using the same account. Avoid storing private keys, passwords or complete access tokens in log messages.
Plan patching, availability and recovery
Maintain the VPN gateway, firewall, operating system and management application. Subscribe to vendor security notices and stage significant updates. A gateway exposed to the internet deserves faster patching than a miner isolated on an internal segment.
Remote control must fail safely. Decide what the miners do when the tunnel, internet, controller or cloud service is unavailable. Local thermal and electrical protections must continue without a remote operator.
Keep a documented local access route, spare gateway configuration and tested key-revocation process. For an unattended site, define who can physically isolate a failed device and how their identity is confirmed.
Test the remote ASIC monitoring VPN
Confirm the public internet cannot reach miner administration directly.
Verify a viewer cannot change pools, firmware or power.
Verify a compromised remote client cannot reach another VPN client or office segment.
Revoke one test user and confirm existing sessions end.
Disconnect the tunnel and confirm local mining protections continue.
Restore the gateway from a protected configuration backup.
Reconcile a test pool change with the audit log and alert.
Repeat tests after firewall, VPN, firmware or network changes. An architecture diagram that was correct before a hosting relocation or router replacement is not evidence of the current path.
When remote access makes sense
A controlled deployment
Remote monitoring makes sense when it reduces travel and downtime while access is segmented, individually authenticated, least-privilege and logged. The operator should be able to explain every permitted path.
Use read-only monitoring for most daily work and elevate only for a specific controlled change.
Reasons to keep administration local
Keep control local when the miner cannot be patched, the only option is public port forwarding, the site has no safe recovery contact or shared credentials cannot be removed.
Remote convenience is not worth connecting an unsupported management surface directly to the internet.
Common remote-monitoring mistakes
Forwarding the miner web port and calling it remote monitoring.
Putting the VPN user into a flat network with office and payment systems.
Sharing one administrator account with staff and suppliers.
Allowing remote control from unmanaged personal devices.
Keeping no log of pool, wallet-destination or firmware changes.
Depending on a cloud controller without a safe local fallback.
Treating VPN encryption as a replacement for patching and least privilege.
Frequently asked questions
What is the main point of remote ASIC monitoring with a VPN?
Remote ASIC monitoring with a VPN: List the actual tasks: view hashrate and temperatures, receive alerts, change pools, restart a miner, update firmware or control power.
For remote ASIC monitoring with a VPN, what should a beginner know about map what remote monitoring must do?
List the actual tasks: view hashrate and temperatures, receive alerts, change pools, restart a miner, update firmware or control power.
For remote ASIC monitoring with a VPN, what should a beginner know about segment the mining network?
Put ASICs and mining controllers on an operational segment separate from office laptops, customer records, finance, WooCommerce, Wi-Fi guests and other internet-connected devices.
For remote ASIC monitoring with a VPN, what should a beginner know about choose the VPN or access architecture?
A site-to-user VPN can work for a small on-premises mine when the gateway is maintained and correctly exposed.
Key points to remember
Secure remote ASIC monitoring with a VPN starts by removing miners from the public internet and placing them in a constrained operational segment. Authenticate the user and device, grant only the required route, protect pool and firmware changes with logs and preserve local recovery.
The goal is not to reach every miner from anywhere. It is to perform a defined task without exposing the rest of the site.
Next steps
Review The Mining Shop UK’s miner security and hosting guidance, then document your current network and ask for technical support before enabling any internet-facing access to an ASIC fleet.
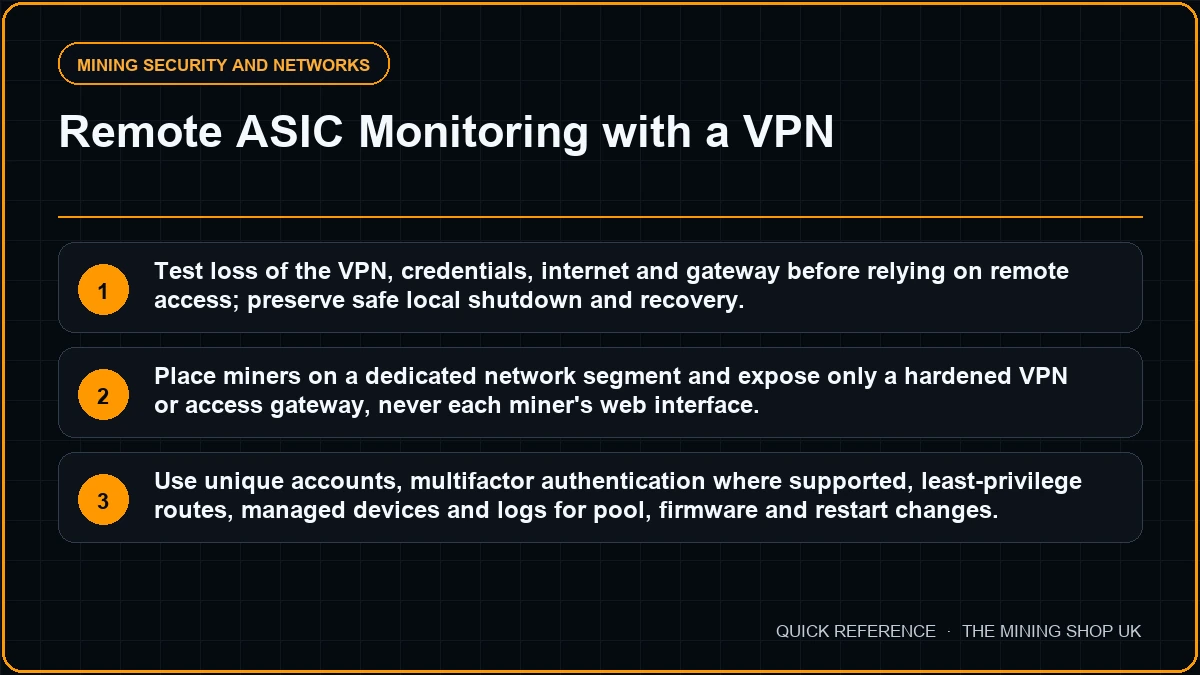
Place miners on a dedicated network segment and expose only a hardened VPN or access gateway, never each miner's web interface. Use unique accounts, multifactor authentication where supported, least-privilege routes, managed devices and logs for pool, firmware and restart changes.
Darren Waggott is the visionary Founder and CEO of The Mining Shop UK, with over a decade of leadership in the cryptocurrency mining sector. Renowned for driving innovation, Darren has built a company dedicated to providing high-quality ASIC miners and comprehensive hosting services. His forward-thinking approach places The Mining Shop UK at the forefront of the industry.
Membership helps us protect the discussion from spam and keep answers useful.
ASIC MINING SUPPORT
Need Help Choosing an ASIC Miner?
Tell us what you want to mine, your electricity cost and where the machine will run. We can help you compare hardware, power requirements, hosting and repairs.
We use necessary cookies to run the shop and optional analytics cookies to understand how visitors use the site and improve shopping and checkout. You can accept analytics, use only necessary cookies, or choose settings. You can change your choice at any time.
Functional
Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes.The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.


Join the ASIC Mining Discussion
Members can read and join the discussion
Log in to read comments from other miners. Create a free account if you would like to ask a question or share your experience.
Membership helps us protect the discussion from spam and keep answers useful.